XRP Ledger patches decade-old bug that could mint XRP
RippleX disclosed an integer-overflow flaw that could create spendable XRP through crafted DEX payments. The emergency xrpld 3.4.1 release fixed it on 25 September.
Listen to this articleListen
RippleX disclosed a critical XRP Ledger flaw on 9 October 2026 that could create spendable XRP through a specially crafted payment. Its security report says the emergency xrpld 3.4.1 release fixed the vulnerability on 25 September.
The bug affected xrpld 3.4.0 and earlier. RippleX says its investigation found no evidence of exploitation on public networks. The team confirmed the behaviour on a local standalone server and in unit tests.
An overflowing total could create a payment imbalance
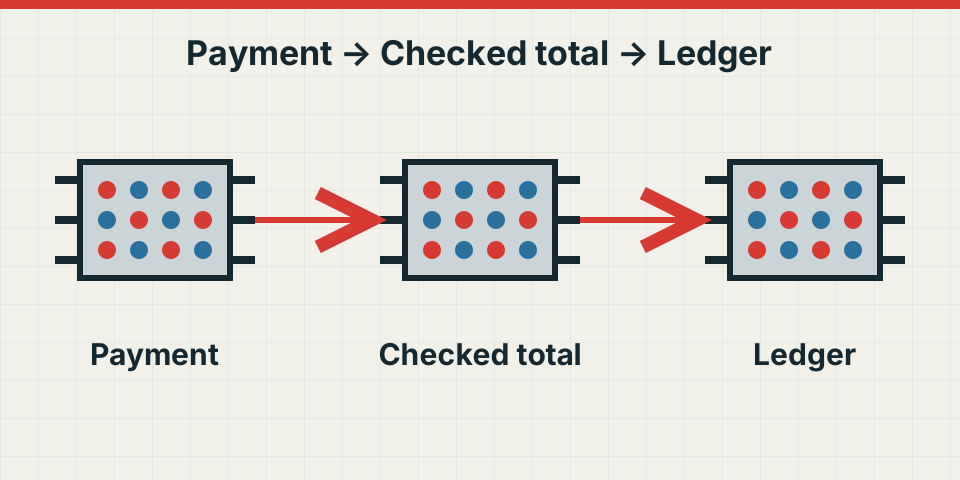
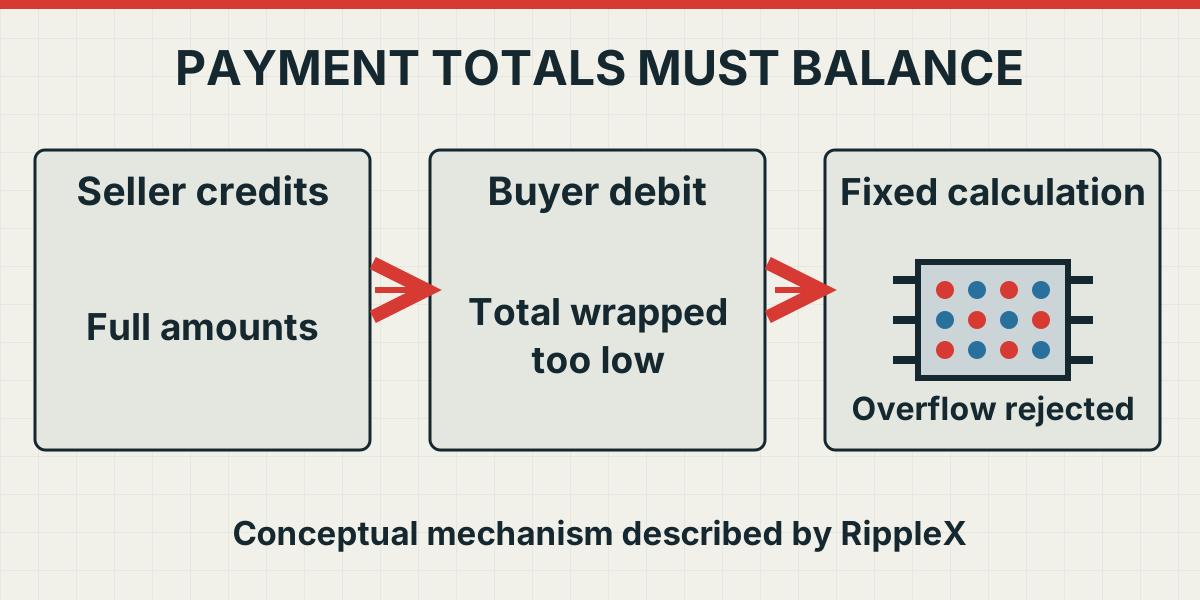
An unchecked 64-bit addition could make the buyer’s total charge wrap to a much smaller number, while sellers received their full amounts. The report describes a crafted set of order-book offers followed by a payment through the ledger’s decentralised exchange.
That difference could produce newly spendable XRP, violating the ledger’s original 100 billion XRP supply. Canary XRP ETF’s annual SEC filing independently describes that fixed original issuance. A separate ledger check intended to catch XRP creation also used vulnerable arithmetic, allowing the imbalance to pass validation.
The investigation traces the flaw to 2015
RippleX says the payment-engine vulnerability appears to have existed since 2015. The investigation also identified the affected invariant check as a later addition.
Researchers reported the bug on 22 September. RippleX reproduced it and raised its severity to critical. The disclosure explains that the created XRP could then be transferred in another payment, establishing a concrete supply-integrity risk.
The emergency release hardened payment arithmetic
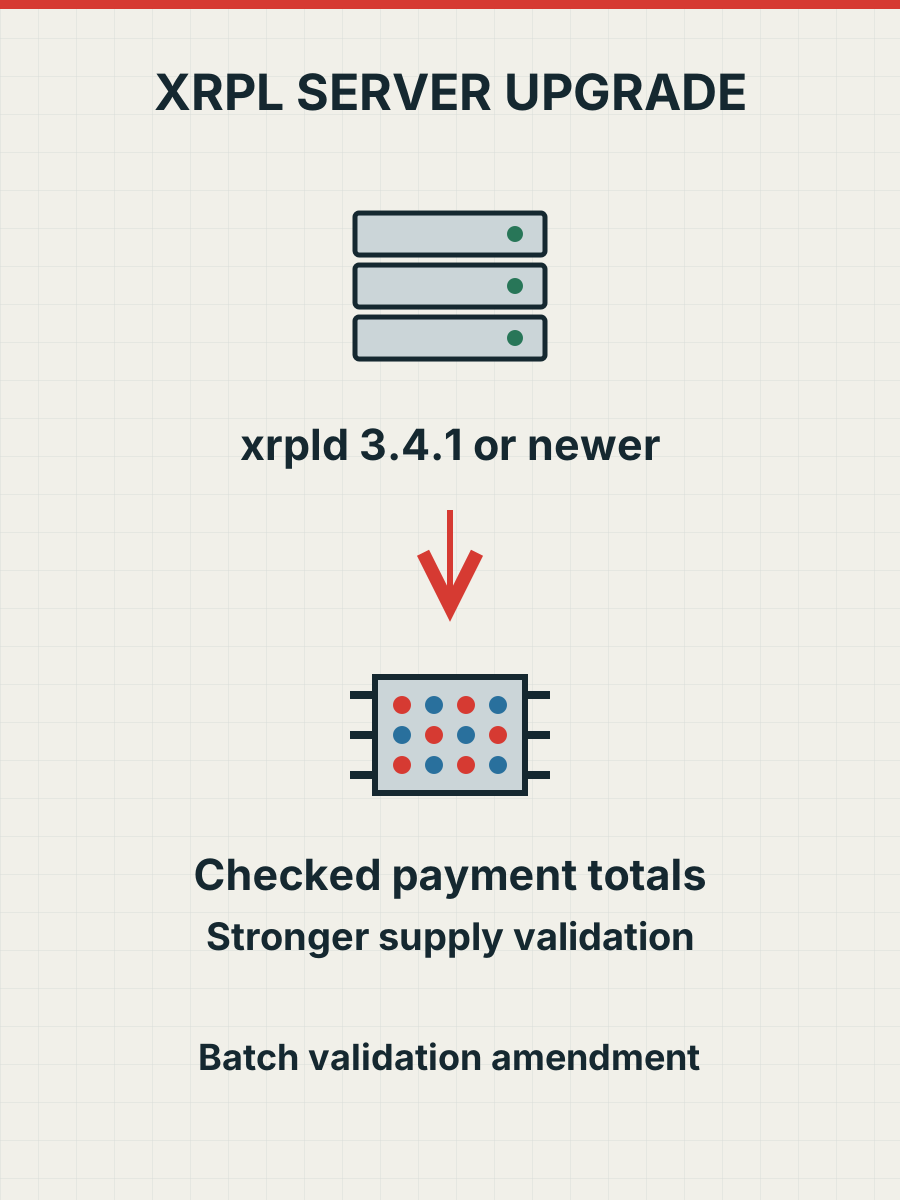
xrpld 3.4.1 added checked arithmetic and strengthened the supply check, according to the 9 October report. Those payment-engine protections take effect when a server upgrades.
The 25 September release notice identified the update as an emergency security release. Its changelog lists integer-arithmetic hardening, while the full explanation followed after operators had time to install the patch.
Server operators need version 3.4.1 or newer
XRPL’s release notice directs operators to upgrade to xrpld 3.4.1 or newer to stay synchronised. The update also introduces fixBatchV1_2, which addresses the validation of wrapped transactions inside a Batch transaction.
The release provides package-installation instructions and amendment-voting guidance. Operators should check the version actually running on each server and follow the official upgrade procedure. The payment arithmetic fix and the Batch amendment have distinct activation mechanisms, both described in the release documents.