Lighter pauses withdrawals after a leaked key drains $10.4 million
An attacker worked out a trader’s API key from public signatures and moved 10.39 million USDC out of Lighter on 16 November 2026. Lighter paused withdrawals, returned about 5 million USDC to the trader and reopened the same day.
Listen to this articleListen
An attacker used a leaked trading key to move 10.4 million USDC out of a trader’s account on Lighter on Monday, and the exchange paused all withdrawals while it investigated. Lighter, a decentralised exchange for perpetual futures, says its protocol, smart contracts and infrastructure were unaffected.
The key leaked through the trader’s own signatures. In an incident report on Monday evening, Lighter said the affected accounts used “unsafe signing code other than the official Lighter SDKs, and that code reused signing nonces, which made the private keys recoverable from public data.” By the evening it had reopened withdrawals and returned about 5 million USDC, roughly $5 million, to the trader.
How did the attacker get the key?
The attacker calculated it from signatures the trader had already made public. Every transaction on Lighter is authorised by a signature from an API key, and each signature uses a one-off random number called a nonce. Lighter’s report sets out the danger: “If the same nonce is used with the same key to sign two different transactions, anyone can calculate the private key from those two signatures.”
The affected accounts were signing with code other than Lighter’s official software kits, and that code reused nonces. So the attacker needed no access to the accounts or to Lighter’s systems, only the public record. Lighter notes that the same weakness applies to Bitcoin and Ethereum signatures.
How did the money leave Lighter?
A Lighter API key can only withdraw to its own account’s wallet, so the attacker routed the money through a public pool. Lighter counts a pool that an account creates as one of that account’s sub-accounts, and a key can move funds into it. According to Lighter, the attacker used the leaked key to create a public pool from the trader’s account and minted pool shares in a separate account it controlled. It then moved the trader’s funds into the pool, which raised the value of those shares, and redeemed them.

The money left in a single Ethereum transaction on Monday morning: 10.39 million USDC, about $10.4 million, from Lighter’s contract to a wallet that Lighter later named as “believed to be associated with the attacker”. Bitquery, a blockchain data company, traced 10.38 million USDC being swapped for about 5,764 ETH, worth about $10.4 million, within the next 35 minutes, most of it through CoW Swap, and part of that ETH moving on to 12 accounts on Hyperliquid, another exchange.
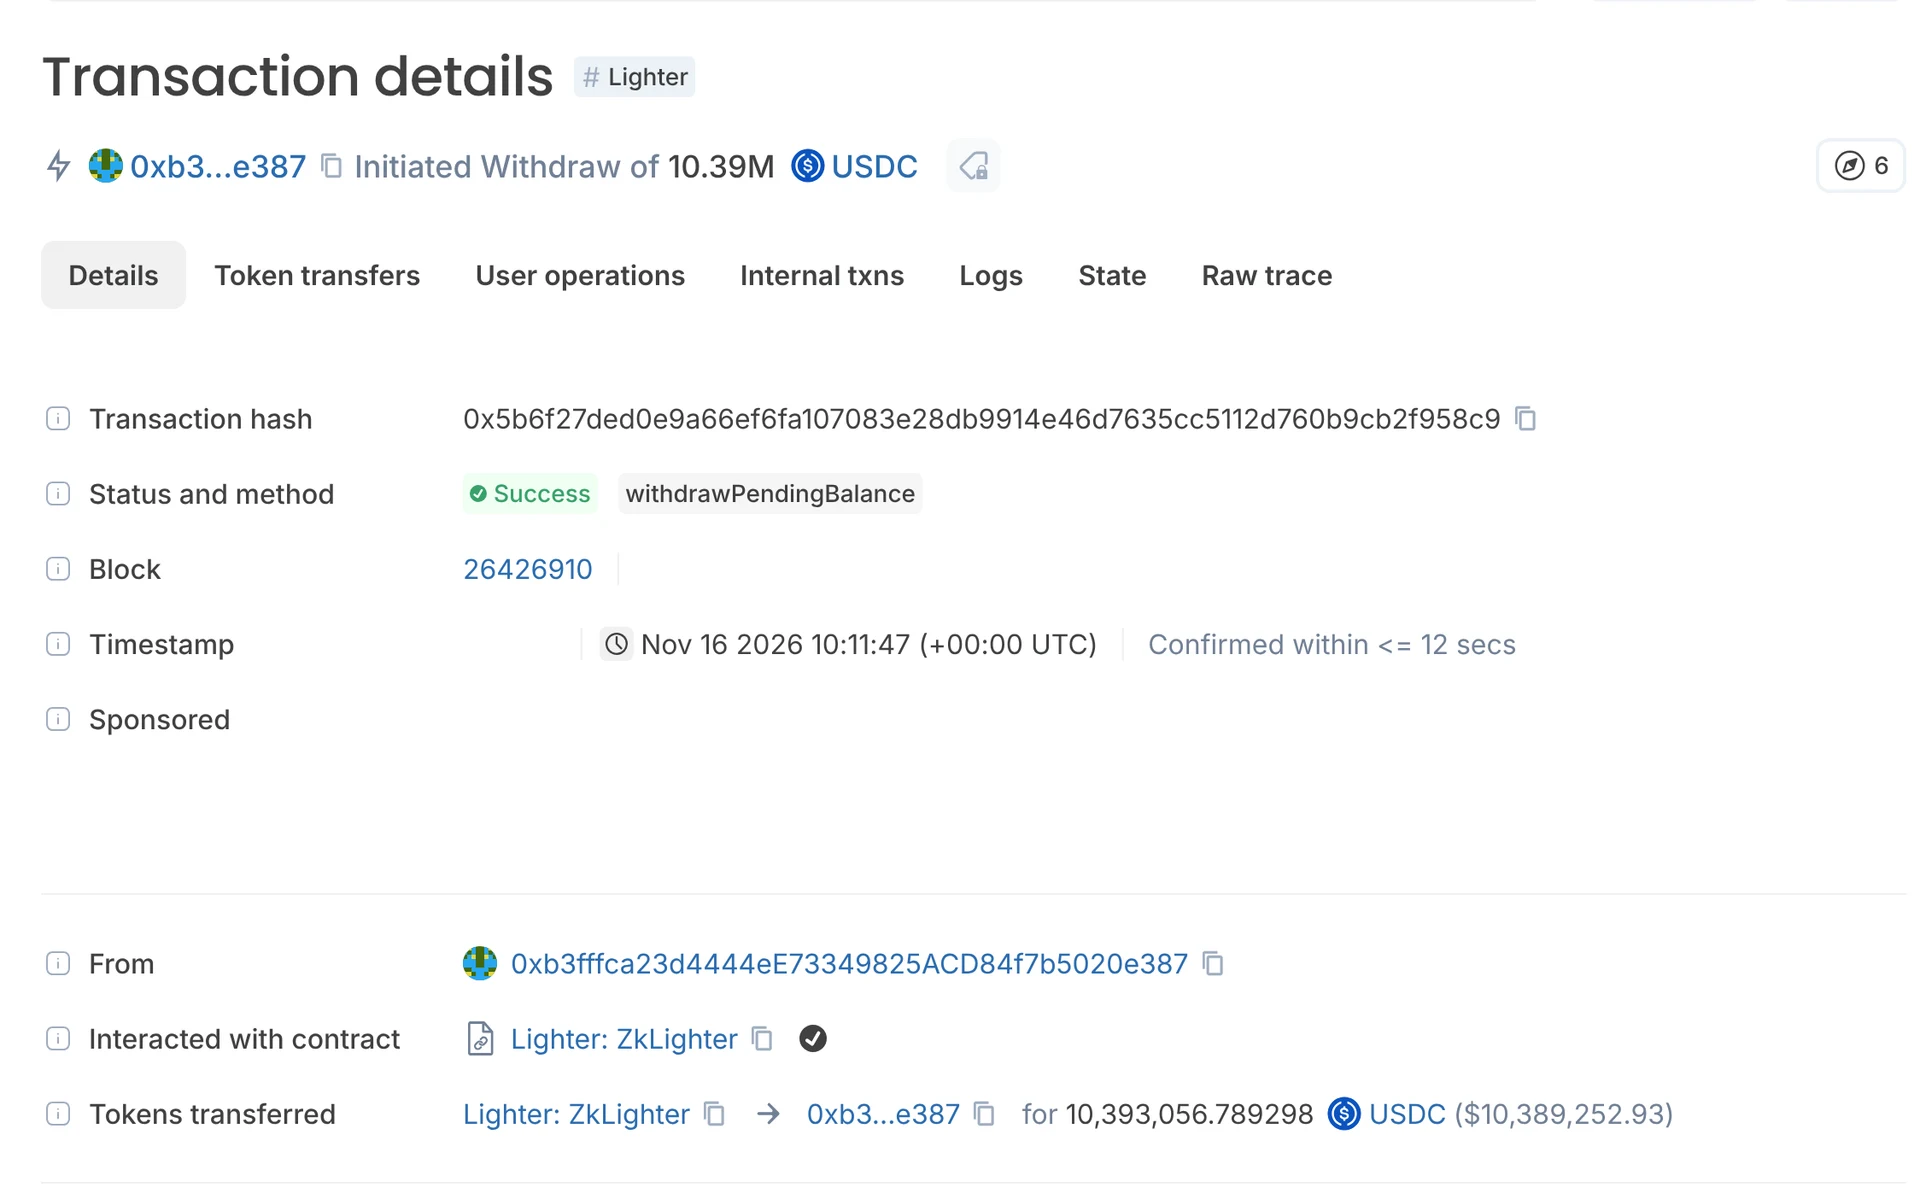
| Event, 16 November 2026 | Time (UTC) | On-chain record |
|---|---|---|
| 10,393,056.79 USDC leaves Lighter’s contract | 10:11:47 | Ethereum block 26,426,910, transaction 0x5b6f27de…f958c9 |
| Receiving wallet, named by Lighter | 0xb3fffca23d4444eE73349825ACD84f7b5020e387 | |
| Largest swap: 5,000,000 USDC sold on CoW Swap | 10:15:11 | transaction 0x2a5f6efd…60d2 |
| Lighter suspends withdrawals and pool creation | by 11:02 | Lighter’s first post |
| Lighter blames a leaked API key | 12:49 | Lighter’s second post |
| Incident report: withdrawals unpaused | 18:20 | Lighter’s report |
Lighter reopened withdrawals the same evening
Lighter’s smart-contract Guardian paused withdrawals and gave the exchange time to return about 5 million USDC to the trader. Its first post said it had “temporarily suspended all withdrawals and pool creation while we investigate the circumstances and assess the full impact.” A second update blamed “a leaked API key for a specific trader’s account”, switched on Guardian mode and said the main priority was to recover funds involved in “an additional withdrawal attempt by the attacker”, with a contract upgrade by the Lighter Security Council.
The evening report said Guardian, “triggered by the anomaly”, had paused withdrawals and let the Security Council return about 5 million USDC to the affected trader. Guardian mode was then switched off, and “all pending withdrawals are being processed.”
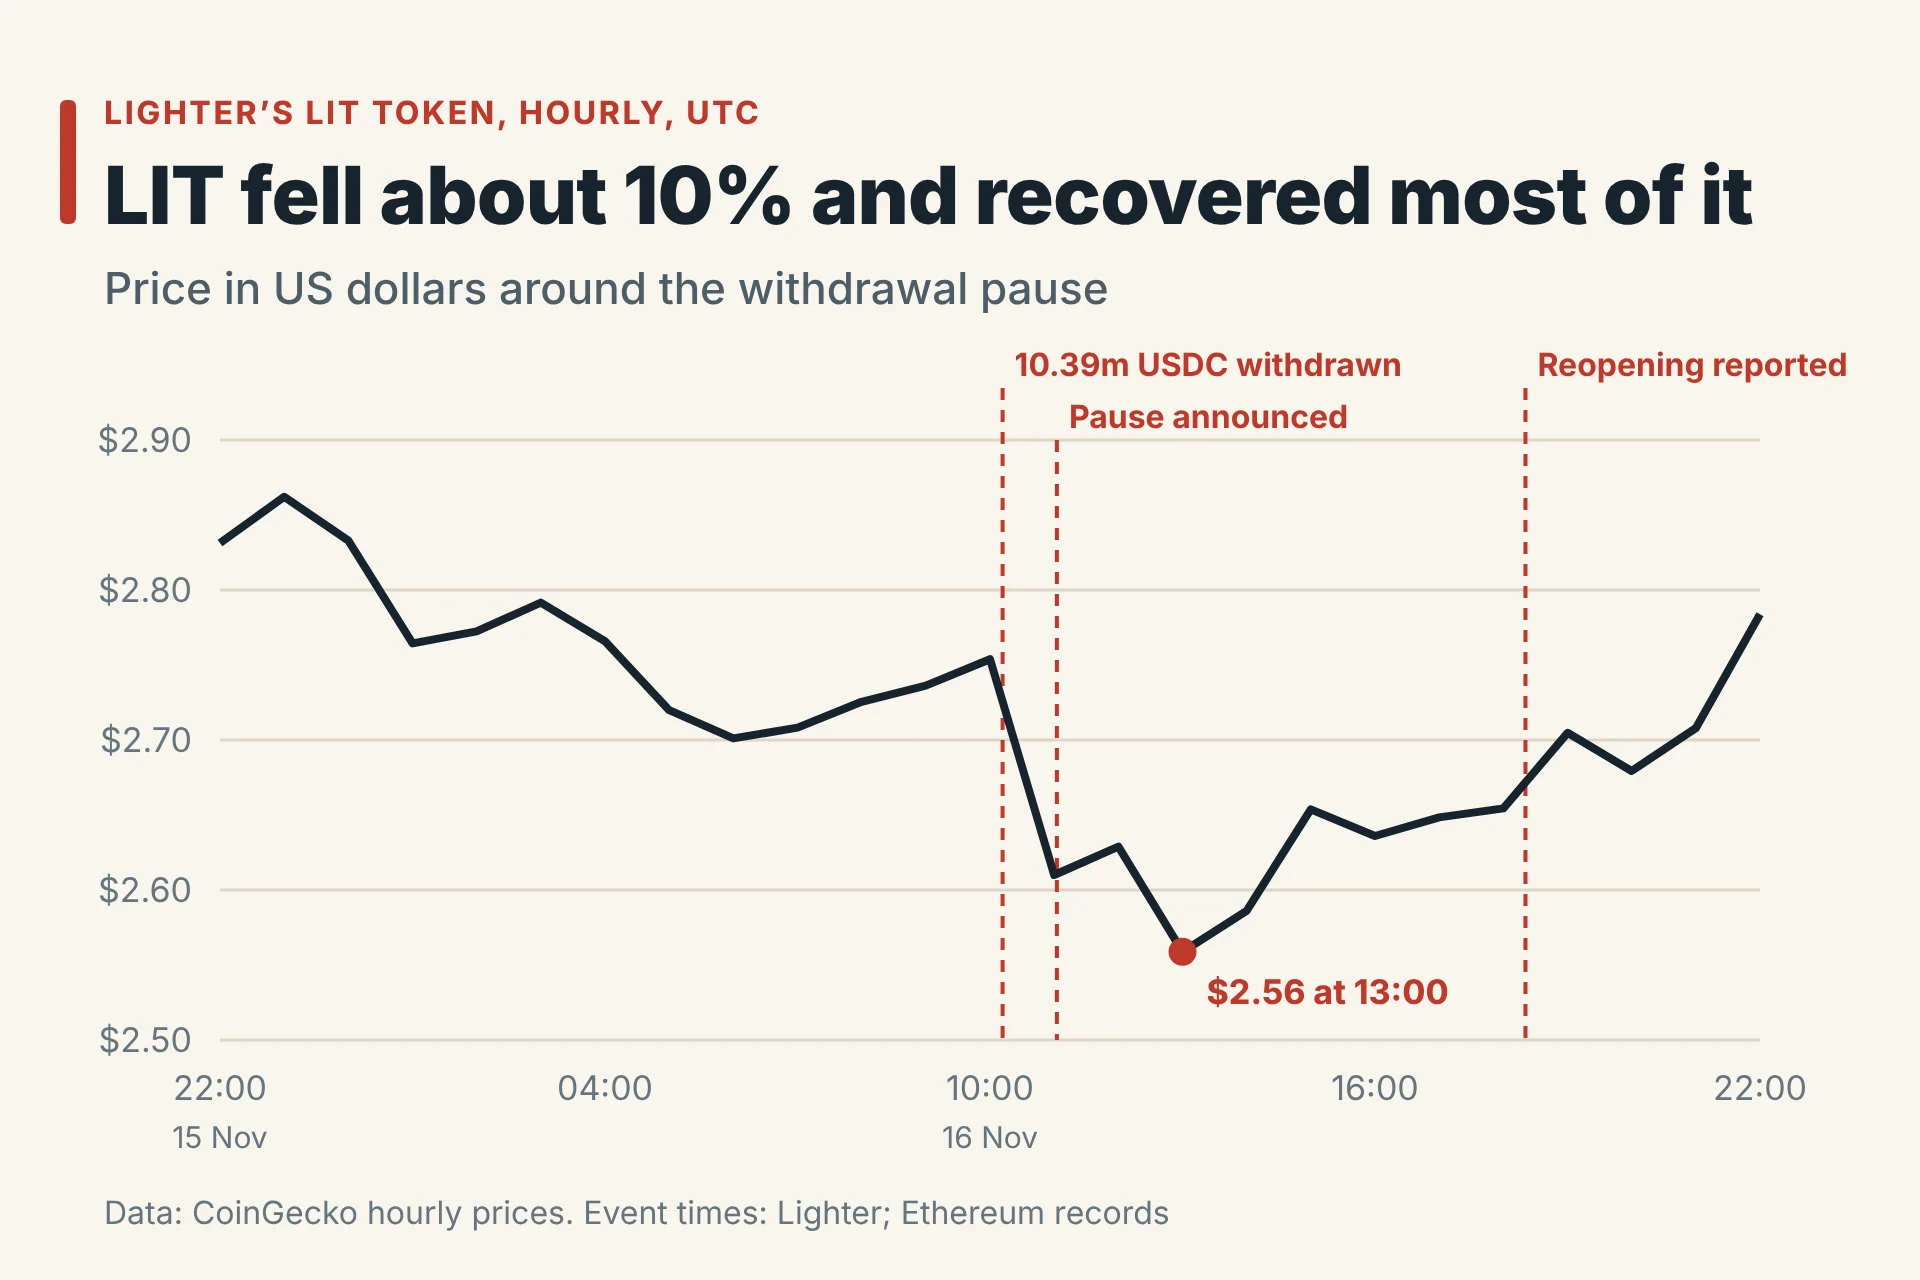
Markets moved and recovered within the day. Lighter’s LIT token fell about 10% between midnight and early afternoon on CoinGecko’s hourly prices, then recovered most of that fall by the evening. Deposits on Lighter fell by about $54 million during Monday on DefiLlama’s figures, a slide that had begun before the attack.
| Measure, 16 November 2026 | Start of day | Later |
|---|---|---|
| LIT price, CoinGecko hourly (UTC) | $2.83 at 00:00 | $2.56 at 13:00; $2.78 at 22:00 |
| Deposits on Lighter, DefiLlama (UTC) | $744.4 million at 00:00 | $690.8 million at 22:16 |
| Returned to the affected trader | about 5 million USDC |
Lighter now needs a wallet signature to fund a pool
Moving money into a public pool now takes the account owner’s wallet signature, so an API key on its own can no longer do it. Lighter has also made API key signatures non-public. Next, it plans restrictions so that a key works only from a server its owner chooses, permissions and limits set for each key, and monitoring for reused nonces, with affected keys voided.
Lighter’s advice is to sign with the official kits
Lighter is telling anyone who trades through code to sign with its official software kits, which it says generate every nonce with a cryptographically secure random number generator. The kits cover Python, Go and TypeScript, plus an agent kit. Anyone unsure whether their own code has ever reused a nonce should rotate all their API keys and switch to an official kit, the exchange says.
An API key alone can authorise withdrawals only to the account owner’s wallet. Sending a fast withdrawal to another wallet also requires the owner’s wallet signature. Lighter warns that whoever holds the API key can still drain value another way: by trading against the owner at bad prices, especially in thin markets, or by loading the account with large, highly leveraged positions.
Sources
- Lighter on X: Signing Safely on Lighter, Lessons from November 16 (incident report)x.com
- Lighter on X: withdrawals and pool creation suspended, 16 November 2026x.com
- Lighter on X: incident caused by a leaked API key, 16 November 2026x.com
- Etherscan: the 10,393,056.79 USDC withdrawal from Lighter’s contractetherscan.io
- Bitquery: Lighter incident investigationbitquery.io
- DefiLlama: Lighter depositsdefillama.com
- Lighter documentation: API keysdocs.lighter.xyz