Railway urges key rotation after possible customer secret exposure
Railway urged customers to rotate credentials after possible access to environment-variable secrets. Deployments were paused and builds began returning in stages.
Listen to this articleListen
Railway has urged customers to rotate credentials after discovering possible unauthorised access to secrets stored in customer environment variables. The hosting platform’s 21 October security disclosure says an outside party may have accessed encrypted values and obtained the decrypted contents of some of them.
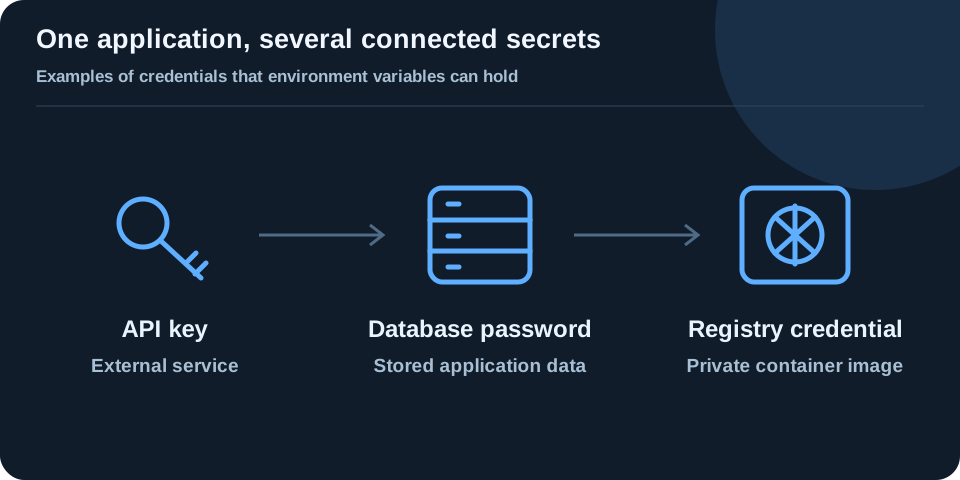
Environment variables are settings supplied to an application when it runs. They can include API keys, database passwords and private registry credentials, giving the incident potential consequences for services connected to an affected project. Railway paused deployments during its investigation and subsequently began restoring builds in stages.
Railway told all users to rotate stored secrets
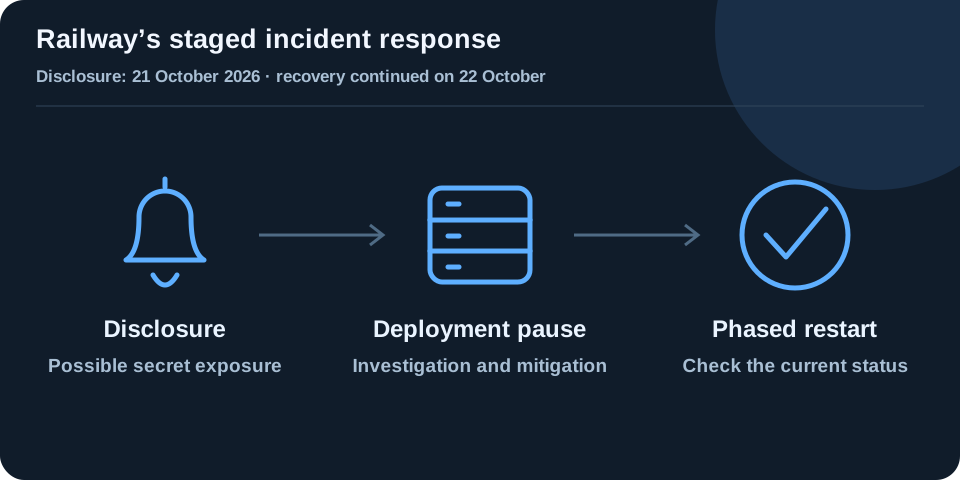
Railway recommended rolling all environment variables containing credentials, including API keys and private registry credentials, and checking service logs for unusual activity. It issued that advice to all users while investigating which accounts were affected.
The company said its initial analysis suggested a subset of customers might be affected. It also said it believed the incident formed part of attacks on platform companies aimed at compromising AI inference providers, and that it had notified upstream providers to revoke keys proactively. That explanation is Railway’s assessment.
The deployment pause complicated recovery
Pausing builds meant customers initially could not deploy new application versions carrying replacement credentials. Railway’s incident log describes a staged restart, beginning with Enterprise workspaces and then Pro, followed by Hobby, Free and Trial.
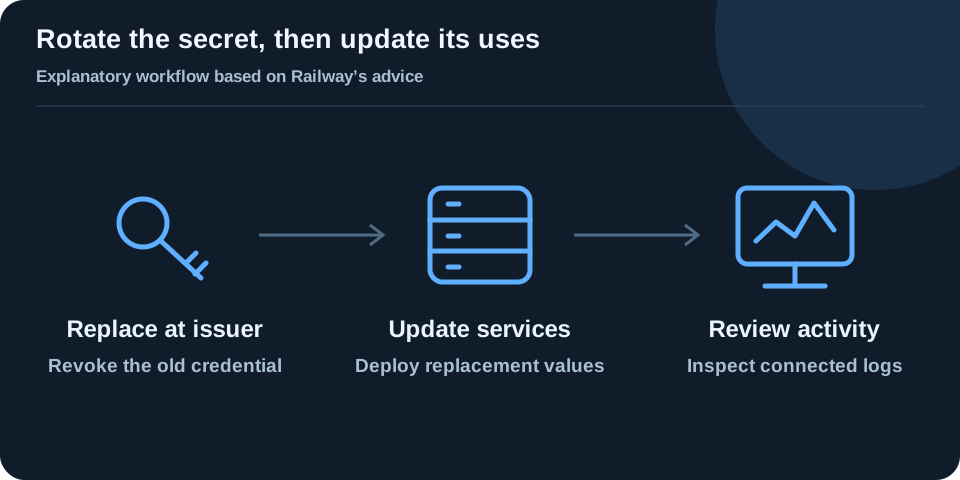
The recovery updates also describe invalidating OAuth sessions as a mitigation and revoking storage-bucket credentials. Customers can use the incident log to check their workspace tier’s build availability as recovery progresses.
Replace the credential at its issuer
Credential rotation requires replacing or revoking the secret at the service that issued it, then updating applications that use it. Changing a variable’s name or moving its existing value leaves the same credential in use.
AWS’s access-key guidance recommends monitoring key usage through CloudTrail and regularly reviewing, updating and deleting access keys. It also recommends temporary credentials where suitable, reducing reliance on long-lived keys.
For Railway customers, the company’s immediate advice combines credential rotation with a review of service activity. Replacement values then need to reach the relevant running services through the restored deployment process.
Sources
- Railway: security disclosure, 21 October 2026blog.railway.com
- Railway: platform outage and recovery updatesstatus.railway.com
- AWS: access-key management and monitoring guidancedocs.aws.amazon.com